Kali AI Pentest
Free version of kali gpt. Works with openai and openrouter key. Openrouter key…
AI runs online
not yet reviewed by publik. It is live now; the founder has not reviewed this version yet.
Where Kali AI Pentest’s AI runs, and what it costs
Prices are for one typical use: one request of about 1,500 words sent and 375 words back. A higher quality score is better.
On your computer
Kali AI Pentest has no option to run its AI on your computer.
publik API
- Price
- $0.0100 per use, $10.00 per 1,000 usespublik-balanced, the default level
- Quality
- MiMo-V2.6-Pro: 46
- Setup
- Not built into Kali AI Pentest yet. A publik API key works wherever Kali AI Pentest takes an OpenAI-compatible address.
Your own key
- Price
- $0.0013 per use, $1.31 per 1,000 usesMiMo-V2.6-Pro at OpenRouter’s list price, before its fee for buying usage
- Quality
- MiMo-V2.6-Pro: 46
- Setup
- Open a provider account, add a card, paste the key into Kali AI Pentest.
Quality and price, side by side
| Model | Quality | Per 1,000 uses |
|---|---|---|
| On your computer (Ollama, 4-bit download size) | ||
| Granite 4.2 3B2.2 GB | 9 | $0 |
| Phi-4 Mini2.5 GB | 6 | $0 |
| Llama 3.1 8B4.9 GB | 7 | $0 |
| gpt-oss 20B14 GB | 9 | $0 |
| Gemma 4 31B20 GB | 19* | $0 |
| Qwen3.5 35B-A3B24 GB | 19* | $0 |
| publik API | ||
| publik-fastGLM-5.3 Flash | 42 | $1.00 |
| publik-balancedMiMo-V2.6-Pro · Kali AI Pentest | 46 | $10.00 |
| publik-smartGPT-6 Sol | 48 | $18.00 |
Quality: Artificial Analysis Intelligence Index v4.3.2, read 2026-09-22 (publik API models 2026-09-25); * = estimated by Artificial Analysis. Sizes: the Ollama library, read 2026-09-22.
What you pay for
- On your computer: nothing per use. You pay in disk space, memory and electricity, at lower quality.
- publik API: publik’s published price for each use, in dollars, from your publik balance. It is above the model’s cost; the difference runs publik and pays the app’s builder.
- Your own key: the provider’s price, billed to an account you keep with the provider.
How to install Kali AI Pentest
Every step written out. No terminal experience needed. Pick your setup.
README
Open in GitHub🐉 Kali AI Pentest Suite
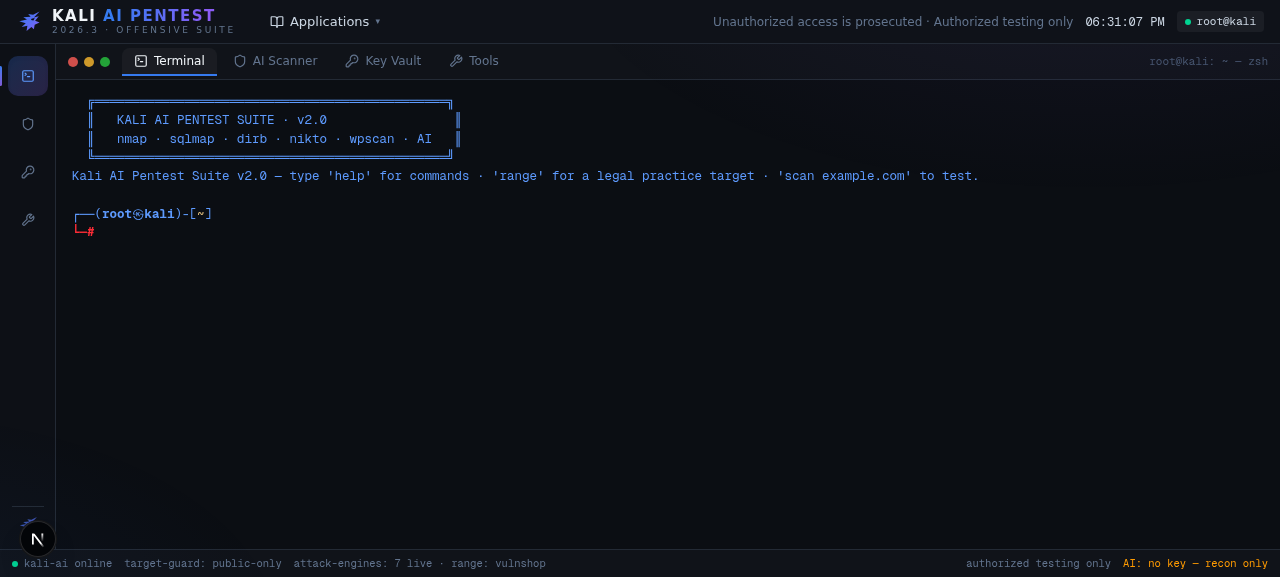
A Kali Linux–styled web suite that scans websites for vulnerabilities with AI — powered by your OpenAI/OpenRouter key, with a built-in engine that works with zero setup.
7 live attack engines · AI copilot · AI attack planner · built-in practice range
✨ Features
| 🖥️ Kali desktop UI | boot sequence, panel, dock, and a real tabbed terminal (tab-completion, history, Ctrl+C/L) |
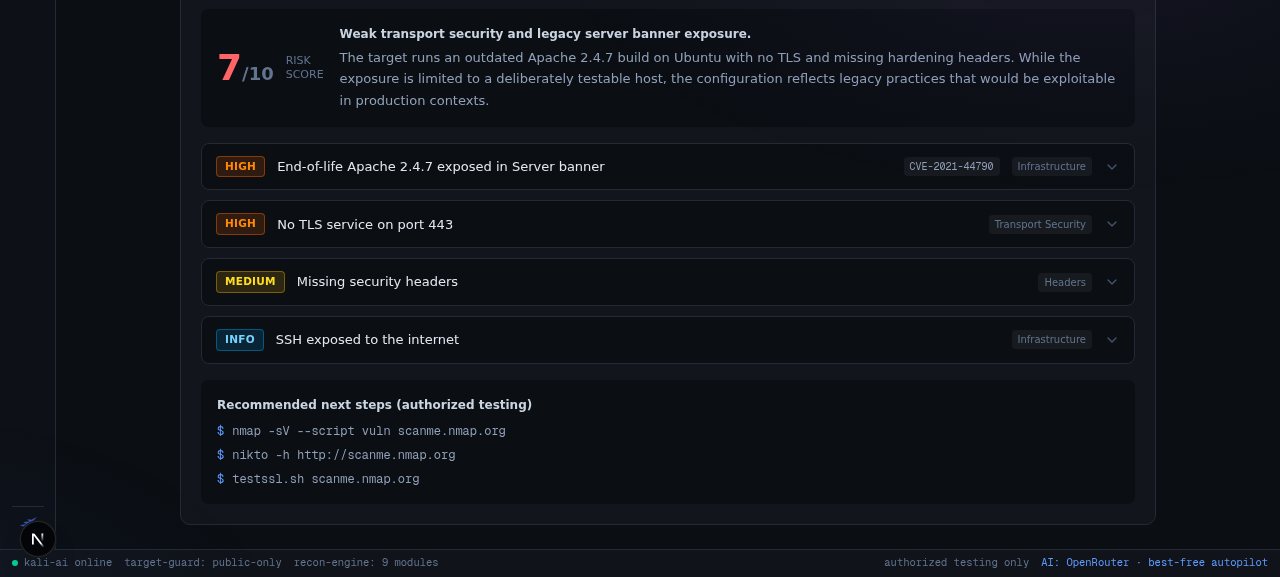
| 🤖 AI vulnerability reports | recon evidence → severity-rated findings, risk score, remediations, next steps (MD/JSON export) |
| 🔑 BYO key + autopilot | OpenAI keys (sk-…) or OpenRouter keys (sk-or-…); OpenRouter always auto-runs the best $0 free model with live failover |
| ⚙️ Built-in engine | no key? every AI feature still works out of the box — and takes over silently if your provider fails |
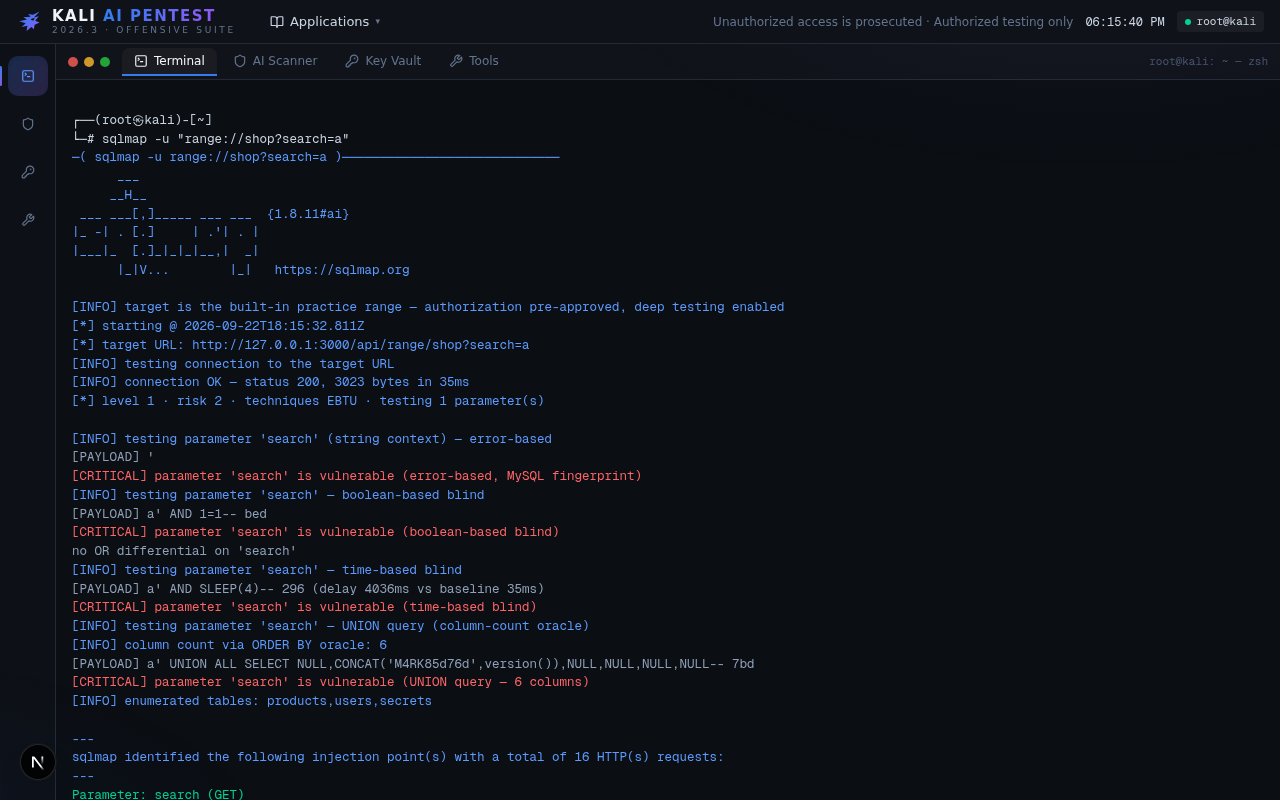
| ⚔️ 7 live attack engines | nmap · sqlmap · dirb/gobuster · nikto · wpscan · searchsploit — pure TypeScript, no binaries required |
| 🧠 AI attack planner | ai plan <target> recons the host, composes a toolchain, executes step-by-step |
| 🧪 VULNSHOP range | deliberately vulnerable local shop (SQLi, auth bypass, exposed .env/.git) to test everything legally |
| 🛡️ Guardrails | authorization gate for active scans, SSRF/private-IP blocklist, read-only payloads by design |
🔑 AI providers
Open the KEY VAULT tab (or ai key <provider> <key> in the terminal):
| Provider | Key format | Behavior |
|---|---|---|
| (none) | — | built-in KAI-SEC engine answers — everything works |
| OpenAI | sk-… | routed to api.openai.com (default model gpt-4o-mini, configurable) |
| OpenRouter | sk-or-… | fetches the live catalogue and always picks the best $0 free model; on 429/errors it fails over to the next free model automatically |
If a provider is unreachable, rate-limited, or the key is rejected, the suite falls back to the built-in engine and says so — requests never hang forever (60s per provider call, 150s overall budget, live KAI is thinking… Ns indicator, Ctrl+C to abort).
Self-hosting the built-in engine: it uses
z-ai-web-dev-sdk, which reads a.z-ai-configJSON file ({"baseUrl": "https://<openai-compatible-endpoint>/v1", "apiKey": "…"}) from the project dir,~, or/etc. See.z-ai-config.example. Without it, just use your own OpenAI/OpenRouter key.
Keys are stored browser-local only (localStorage) and sent per-request to the backend — never persisted server-side, never committed.
🕹️ Usage
Terminal (main tab):
scan <target> [--deep]      full recon + AI vulnerability report
ai ask <question>           security copilot Q&A
ai plan <target>            AI attack toolchain → run <n> to execute
nmap / sqlmap / dirb / gobuster / nikto / wpscan / searchsploit
range                       show the built-in practice target + recipes
help
AI Scanner tab: enter a target, tick the authorization box, watch the live recon pipeline, and get a formatted vulnerability report (risk score, findings, next steps) with Markdown/JSON export.
🏗️ Architecture
- Next.js 16 (App Router) + TypeScript + Tailwind 4 · NDJSON streaming APIs
- Attack engines are pure TypeScript (
src/lib/pentest/) — no native binaries, so it runs anywhere Node runs: TCP connect scans with service/OS detection, SQLi (error/boolean/time/UNION), content discovery (500+ wordlist), web misconfig scanner, WordPress enumerator, offline exploit DB - AI layer (
src/lib/ai.ts): provider chain → OpenAI → OpenRouter best-free → built-in engine, with bounded timeouts and JSON repair
src/
├── app/api/          exec · tools · recon · pentest · range · ai/{chat,plan,analyze} · openrouter/models
├── components/kali/  boot · desktop shell · terminal · scanner · key-vault · tools-grid
└── lib/              target-guard (SSRF blocklist) · recon pipeline · pentest engines · ai · openrouter
⚠️ Legal & responsible use
This tool is for authorized security testing only — your own systems or targets you have written permission to assess. Active tools require a --auth acknowledgment for public targets; private/loopback ranges are blocked. Do not scan systems you do not own. The built-in VULNSHOP range exists so you can learn and demo safely.
📄 License
MIT — see LICENSE.